For a private voice call, compare the protection documented for the exact call mode: Signal describes end-to-end encrypted calls, WhatsApp documents protection for personal calls, and Discord documents end-to-end encryption for supported non-Stage audio and video. Public social rooms serve a different purpose. No single platform is “most secure” for every audience, device and threat.
Last updated:
This guide appears on SUGO’s own blog. It compares published protection boundaries and practical checks, not independent penetration tests or incident rates. A verified encryption mode can protect the connection without proving that another participant is honest or that their device cannot record what they hear.
What Makes a Voice Platform Secure?
Start with what you are trying to keep private and from whom. A call among known contacts, a server channel with changing membership and an open room for meeting strangers have different audiences. A feature that makes discovery easier may be unsuitable for a confidential discussion. Choose the audience and mode before comparing brand claims.
Distinguish encryption in transit from end-to-end encryption. The latter is intended to make content available to the communicating endpoints rather than an intermediary. It does not automatically describe every feature, stored copy, metadata field or business interaction in the same app. Read the documentation for the call you will actually make.
Compare documented call modes, not a general security label
| Service / mode | What its official material establishes | What remains to check |
|---|---|---|
| Signal calls | The service documents end-to-end protection for conversations and calls. | Confirm the intended contact and any verification change; decide who can join a shared call link. |
| WhatsApp personal calls | Its published material describes end-to-end protection for personal messages and calls. | Verify the contact, participant list and account controls; do not extend that statement to every business or public feature. |
| Discord non-Stage audio/video | Current documentation covers DMs, group DMs, voice channels and Go Live, with encryption information and participant verification. | Check the actual session type and supported client. Stage channels are a documented exception. |
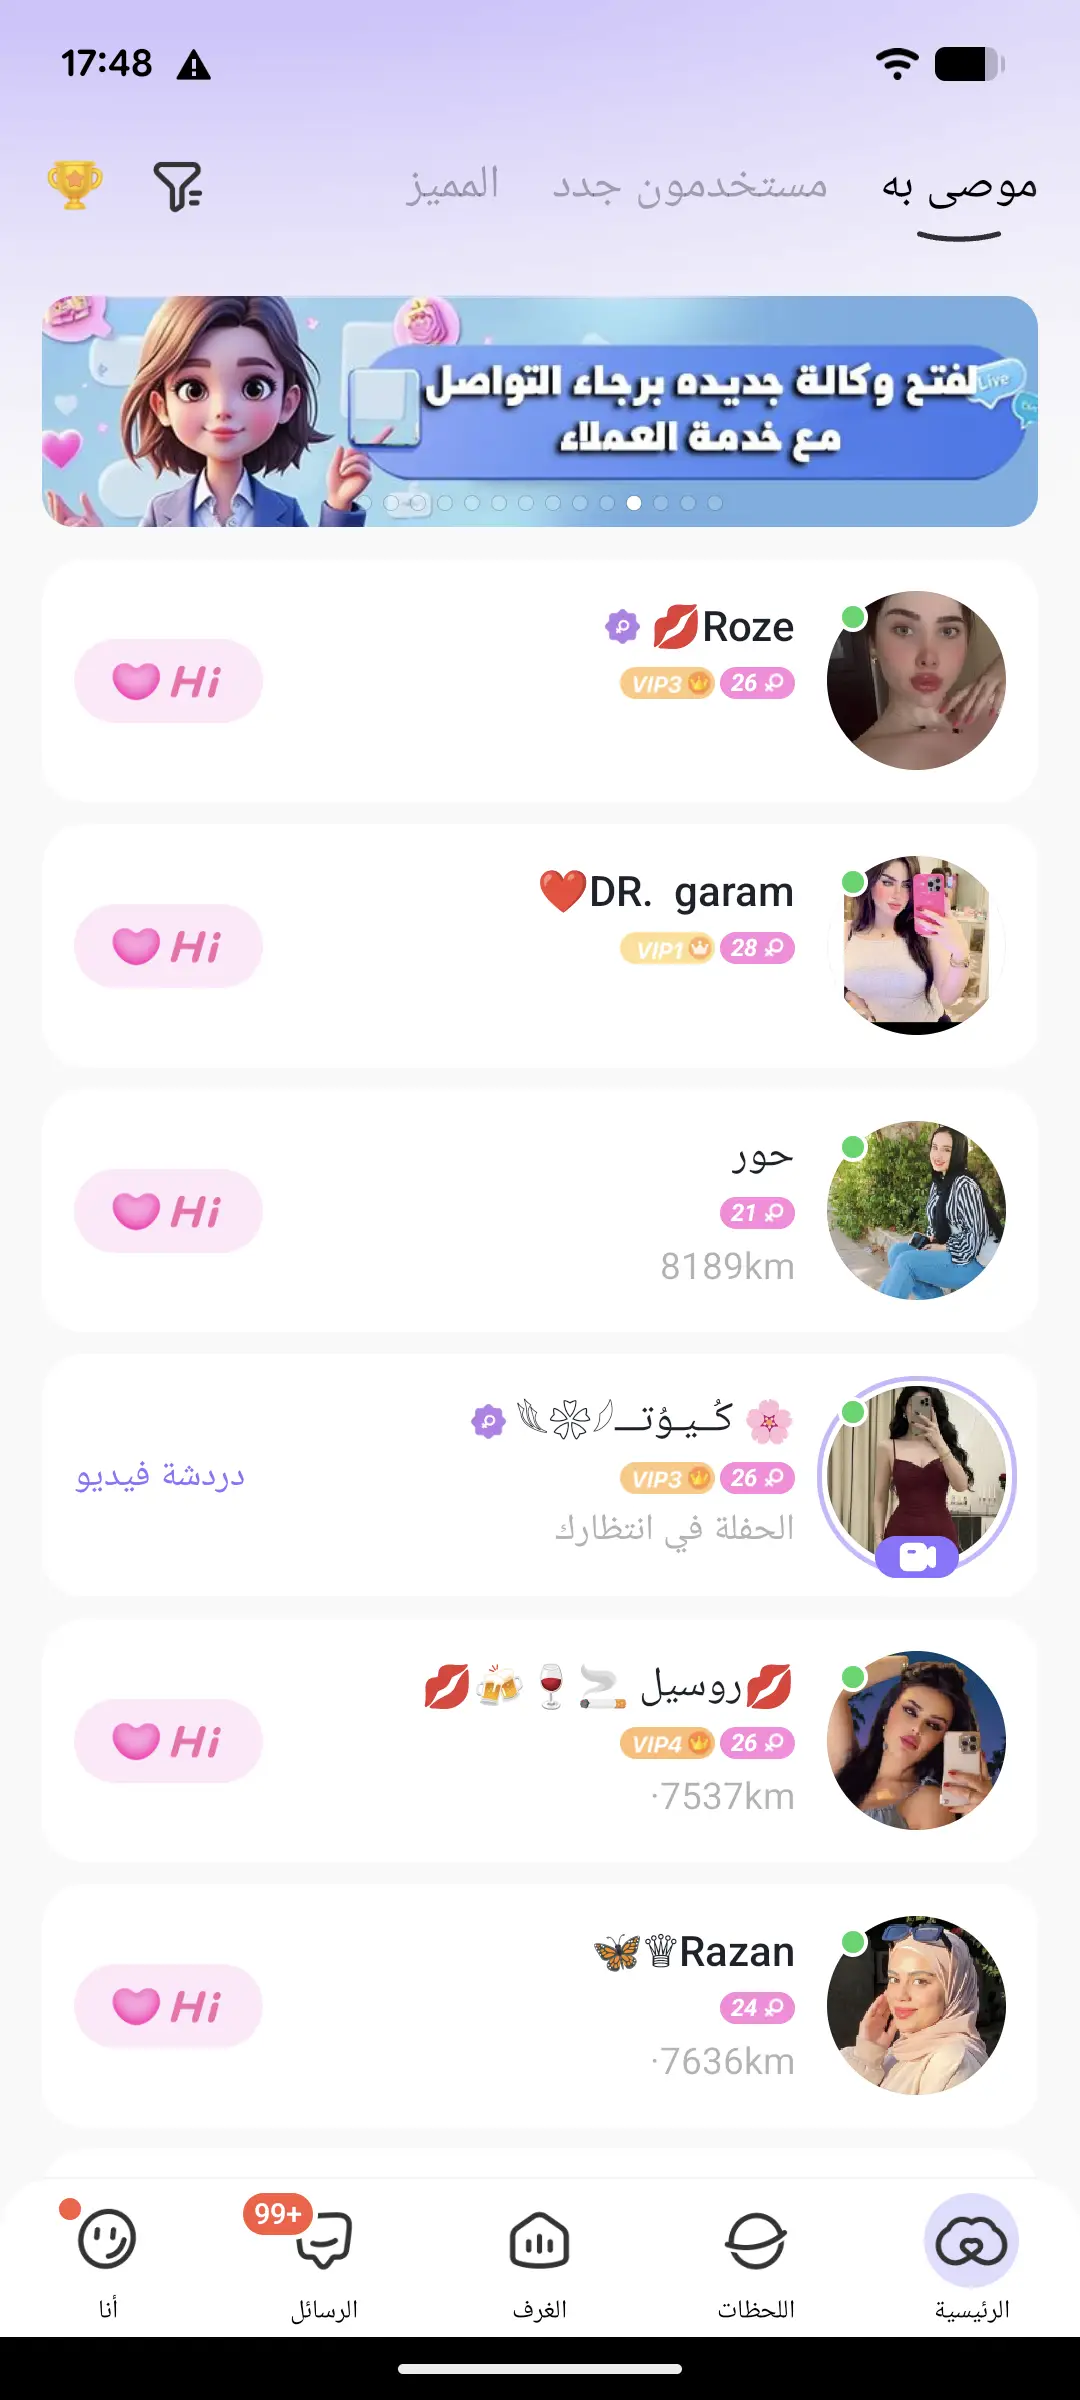
| SUGO social voice rooms | Public material describes social conversation, room participation and virtual gifts. | The sources reviewed here do not establish end-to-end confidentiality for every room. Treat the audience as participants you may not know, not a confidential-call service. |
Signal’s privacy explanation and calling help document its call protection. If you share a call link, use the documented approval controls where appropriate; a reusable invitation is an access decision, not proof that everyone who obtains it is an intended guest.
WhatsApp’s official description explicitly discusses personal messages and calls. Use its account and safety controls alongside that content protection. A familiar profile picture or number should not substitute for independently checking an unexpected request.
Discord’s audio/video encryption help explains call and participant verification. Its current rollout explanation identifies Stage channels as an exception. Do not turn the presence of a server or a voice feature into a blanket encryption statement about every session or text message.
Separate content privacy, account access and audience control
An encryption indicator answers a narrower question than “Can I trust this room?” Account protection helps reduce unauthorized access; participant controls determine who is admitted; blocking and reporting address unwanted behavior. None of those controls makes every shared detail safe to disclose. Review them separately instead of scoring a service by how reassuring its interface feels.
| Your concern | Evidence to examine | A safer next step when unclear |
|---|---|---|
| Someone on the network intercepting call content | The vendor’s documentation and the actual session’s encryption information. | Use a documented protected mode on updated supported clients before sharing private content. |
| An unintended participant joining | The participant list, invite-link handling and approval settings available for that mode. | Stop the sensitive part of the discussion and review invitations or start a new controlled session. |
| A known account behaving unexpectedly | A separately confirmed contact route and any verification-change notice. | Check the request outside the unexpected conversation; do not send passwords or codes. |
| Recording or disclosure by a recipient | Who is present, what they receive and the limits of your agreement with them. | Share less; do not rely on a private-room label or disappearing interface to prevent copying. |
| A device or account compromise | Device access, linked sessions and the vendor’s recovery guidance. | Use the official recovery process and a trusted device where needed; changing a room title does not fix account access. |
What can you verify about SUGO?
SUGO’s privacy policy describes information handling and permissions, while its terms govern use. These are relevant reading before joining, but they do not provide an independent security benchmark or establish a public room as an end-to-end confidential call. A private-room feature, an HD voice description and an identity badge are different claims.
SUGO may be relevant when you want adult social voice interaction. Use it for that purpose after checking the actual room and account controls; do not choose it for confidential material on the strength of an undocumented encryption label. Its terms require at least 18 and local majority. Those age requirements are not evidence that every participant complies or that no abuse will occur.
A short check before a private call
- Agree on who is supposed to join and what can be discussed. Use the service and mode documented for that need.
- Update to a supported client and open the call’s available encryption or participant-verification information. Follow the vendor’s current instructions rather than a screenshot from another version.
- If a verification key or known account changes unexpectedly, confirm the person through a route you already trust before sharing sensitive details.
- Review the actual participant list and invitation controls. A group name is not a list of everyone who can hear.
- If the protection or audience cannot be established, pause the private topic and choose another documented mode. Keep only the minimum support information needed to investigate the issue.
This is a decision checklist, not a test result for these products. A successful ordinary call confirms that people can connect; it does not prove the security of the service. Equally, poor audio or a failed connection does not by itself identify an encryption failure or an attack.
Moderation and privacy solve different problems
A moderator may remove an abusive participant, but that is not the same as protecting call content from an intermediary. End-to-end encryption can protect content while a recipient still makes a fraudulent request. Decide which problem you are responding to, and use the relevant reporting, access or verification controls.
Signal’s scam and impersonation guidance makes that distinction explicit: strong encryption does not stop social engineering. For requests encountered through SUGO, the separate authentication and scam guide covers behavior and account checks without treating a natural voice or badge as proof of trust.
What a comparison can and cannot establish
An old protocol roundup, a vendor’s enterprise sales page and a current consumer-call help page answer different questions. Do not carry a historical app list, a government compliance claim or a protocol’s reputation over to a different product or mode. Current call documentation is the starting point; a claim of superior security would need a clearly scoped, independent assessment.
This guide supplies no personal testing history, SUGO internal audit or comparative incident rate. It therefore does not rank the services as universally safest or describe confidence as a form of encryption. Product descriptions, a user’s call check and a security audit should remain distinct evidence.
Conclusion
Choose the documented protection for the audience and call mode you need, then verify the participants and access controls. For social discovery, keep sensitive information out of ordinary rooms. For confidential conversation, use a mode whose protection you can establish instead of relying on a general “secure voice” promise.
More guides on this topic: Scams, Fake Profiles and Verification
FAQs
What is the safest type of voice platform?
There is no universal answer. For a private call, start with documented end-to-end protection for the exact mode, then check the contact, participant list and account access. A public social room has a different audience and should not be treated as confidential merely because it offers a private-looking interface.
Does encryption protect everything?
No. Content protection does not automatically cover every metadata field, stored copy, account setting or recipient action. A participant may still record what they hear or make a deceptive request. Check the documented scope and share only what is appropriate for the actual audience.
Are all Discord audio rooms end-to-end encrypted?
Discord documents end-to-end encryption for supported non-Stage audio/video sessions, including the types listed in its current help. Stage channels are an explicit exception. Check the session type and current client rather than assuming that every server feature has the same protection.
Is a SUGO private room proof of end-to-end confidentiality?
The public sources reviewed here do not establish that conclusion. Room access, voice quality, identity checks and encryption are separate properties. Check official information for the actual mode and avoid sensitive disclosures when its protection or audience cannot be established.
Can an encrypted call still involve a scam?
Yes. An encrypted connection can carry a dishonest request from a recipient. Independently verify unexpected demands, keep passwords and login codes private, and use the service’s official blocking, reporting or recovery route when appropriate.